From fragmented alerts to
one unified security truth.
The agentic AI operating layer for security operations.
Security leaders face a paradox more tooling than ever, yet threats slip through. SPoG unifies signals from SIEM, EDR, Firewall, Cloud, Identity and Threat Intelligence into one operating layer that doesn't just surface the picture it orchestrates the response and acts on it.
60%
Reduce MTTD
75%
Less False Positives
6–10
Weeks To First Outcomes
100+
Companies Served Since 2014
You've invested in the tools. The threat is still winning.
Every security operation runs dozens of controls across endpoint, network, cloud and identity, yet analysts still spend hours chasing false positives and correlating alerts manually. The gap isn't more tooling it's the operating layer that turns signal into action.
Alert Overload
SOC teams drown in thousands of alerts daily across SIEM, EDR and cloud platforms, with no unified context to distinguish noise from genuine threats.
Slow Detection & Response
Manual investigation across disconnected tools increases dwell time, delays response and exhausts analyst capacity.
Rip-and-Replace Fatigue
Another security platform isn't the answer. Unlock value from the tools you already own through one intelligent operating layer.
Unify your signals. Automate your response. Accelerate security outcomes.
Transform fragmented security tooling into one AI-driven operating layer that delivers detection, orchestration and response with complete executive control.
The Single Pane is not another security dashboard.
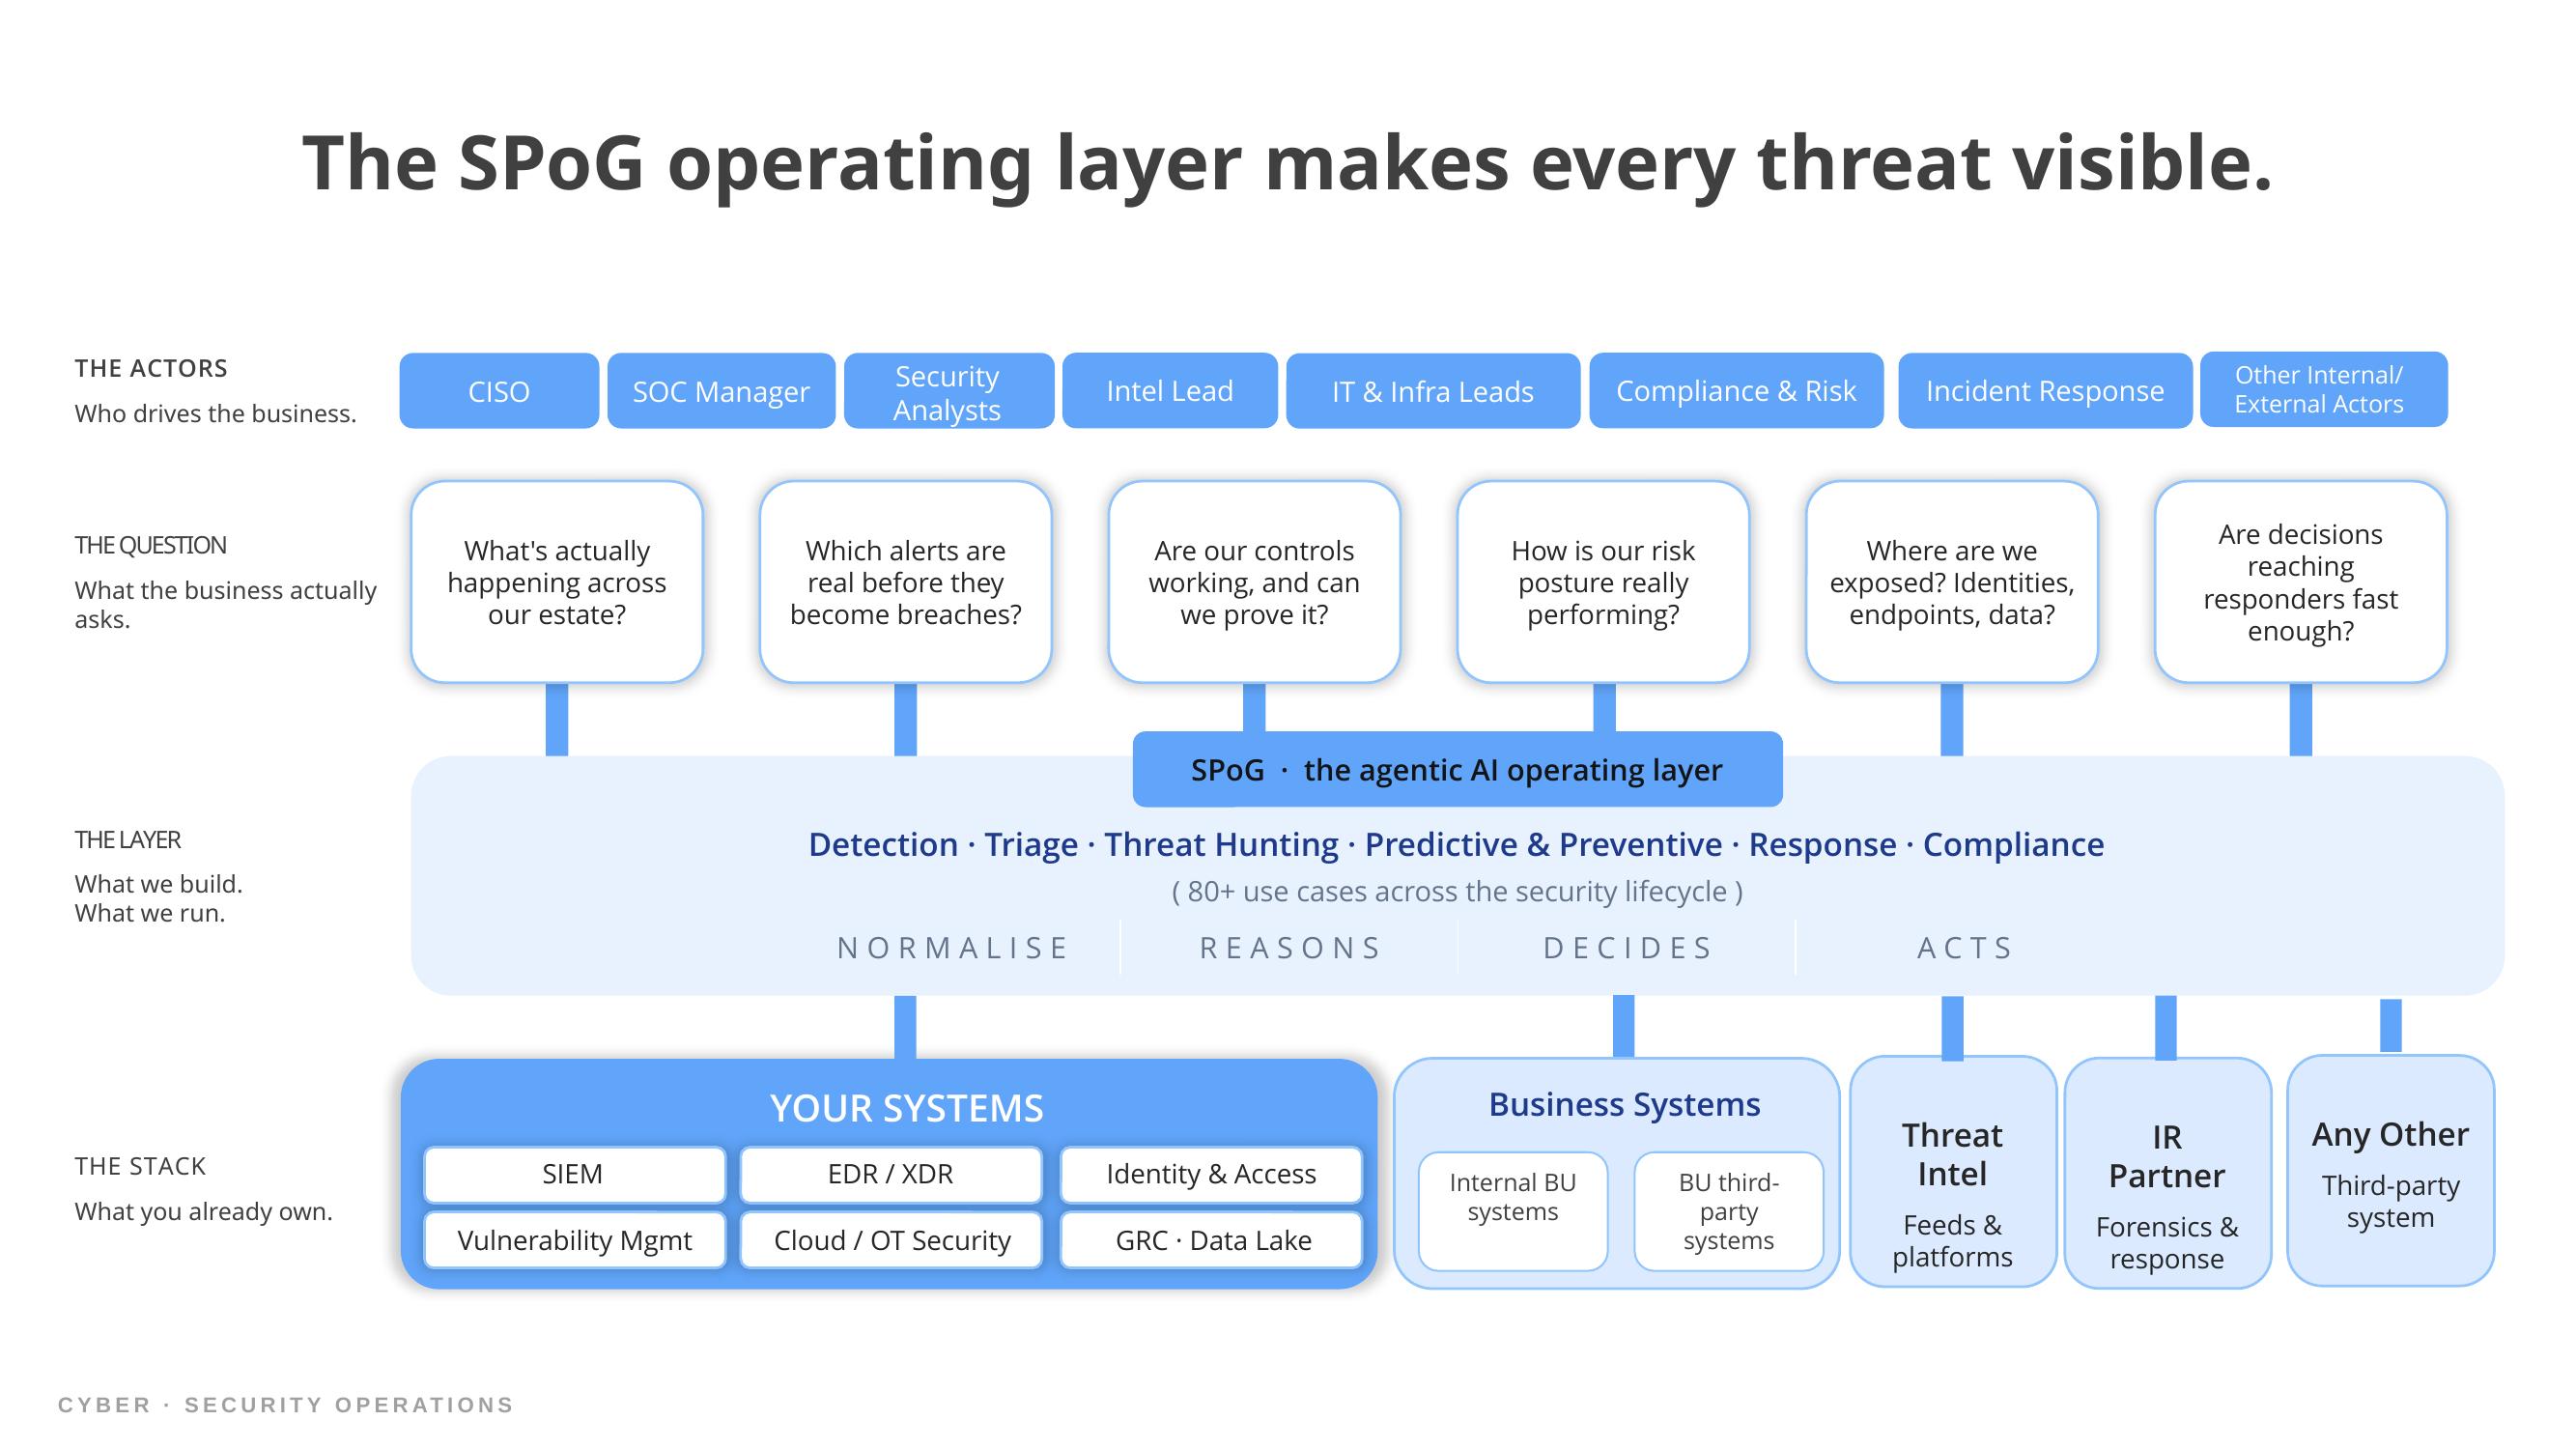
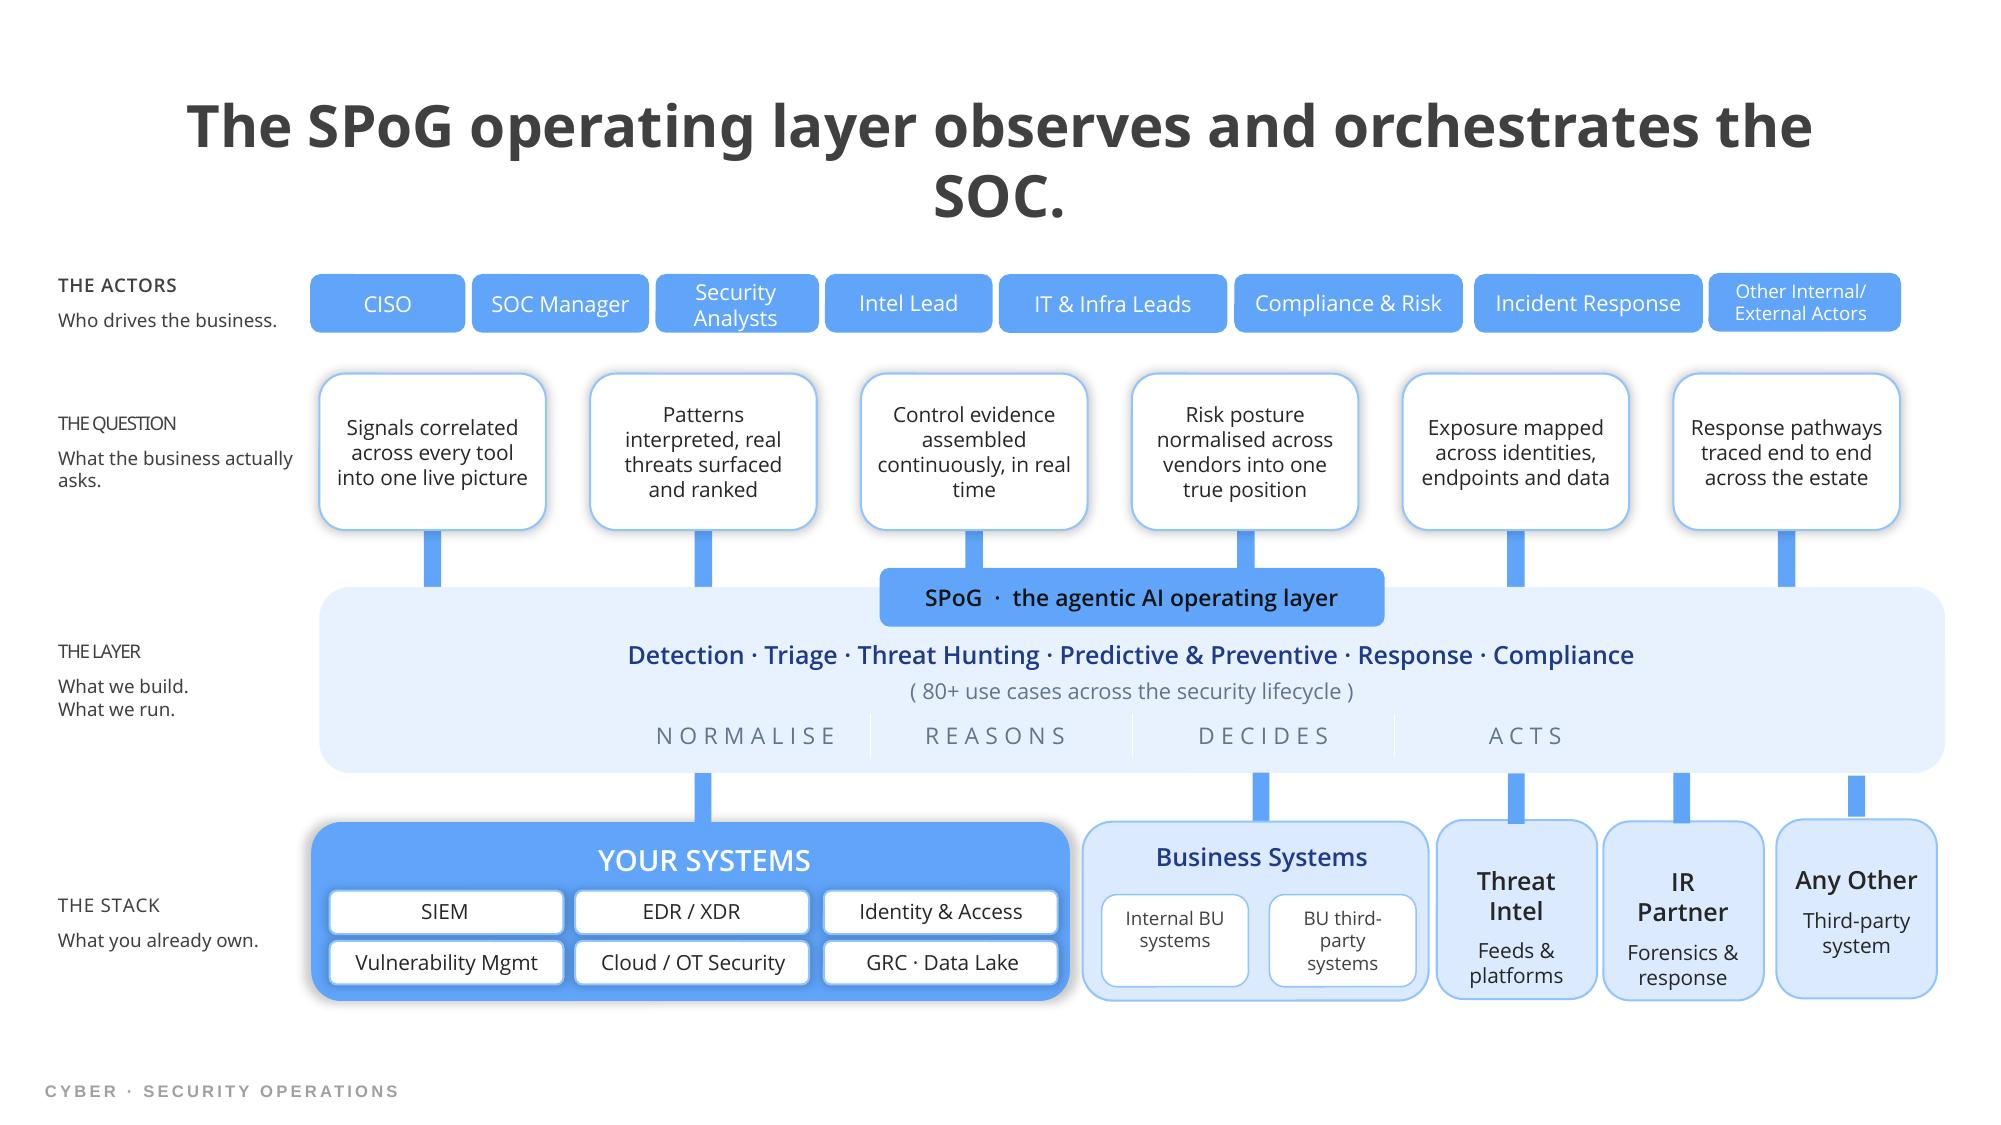
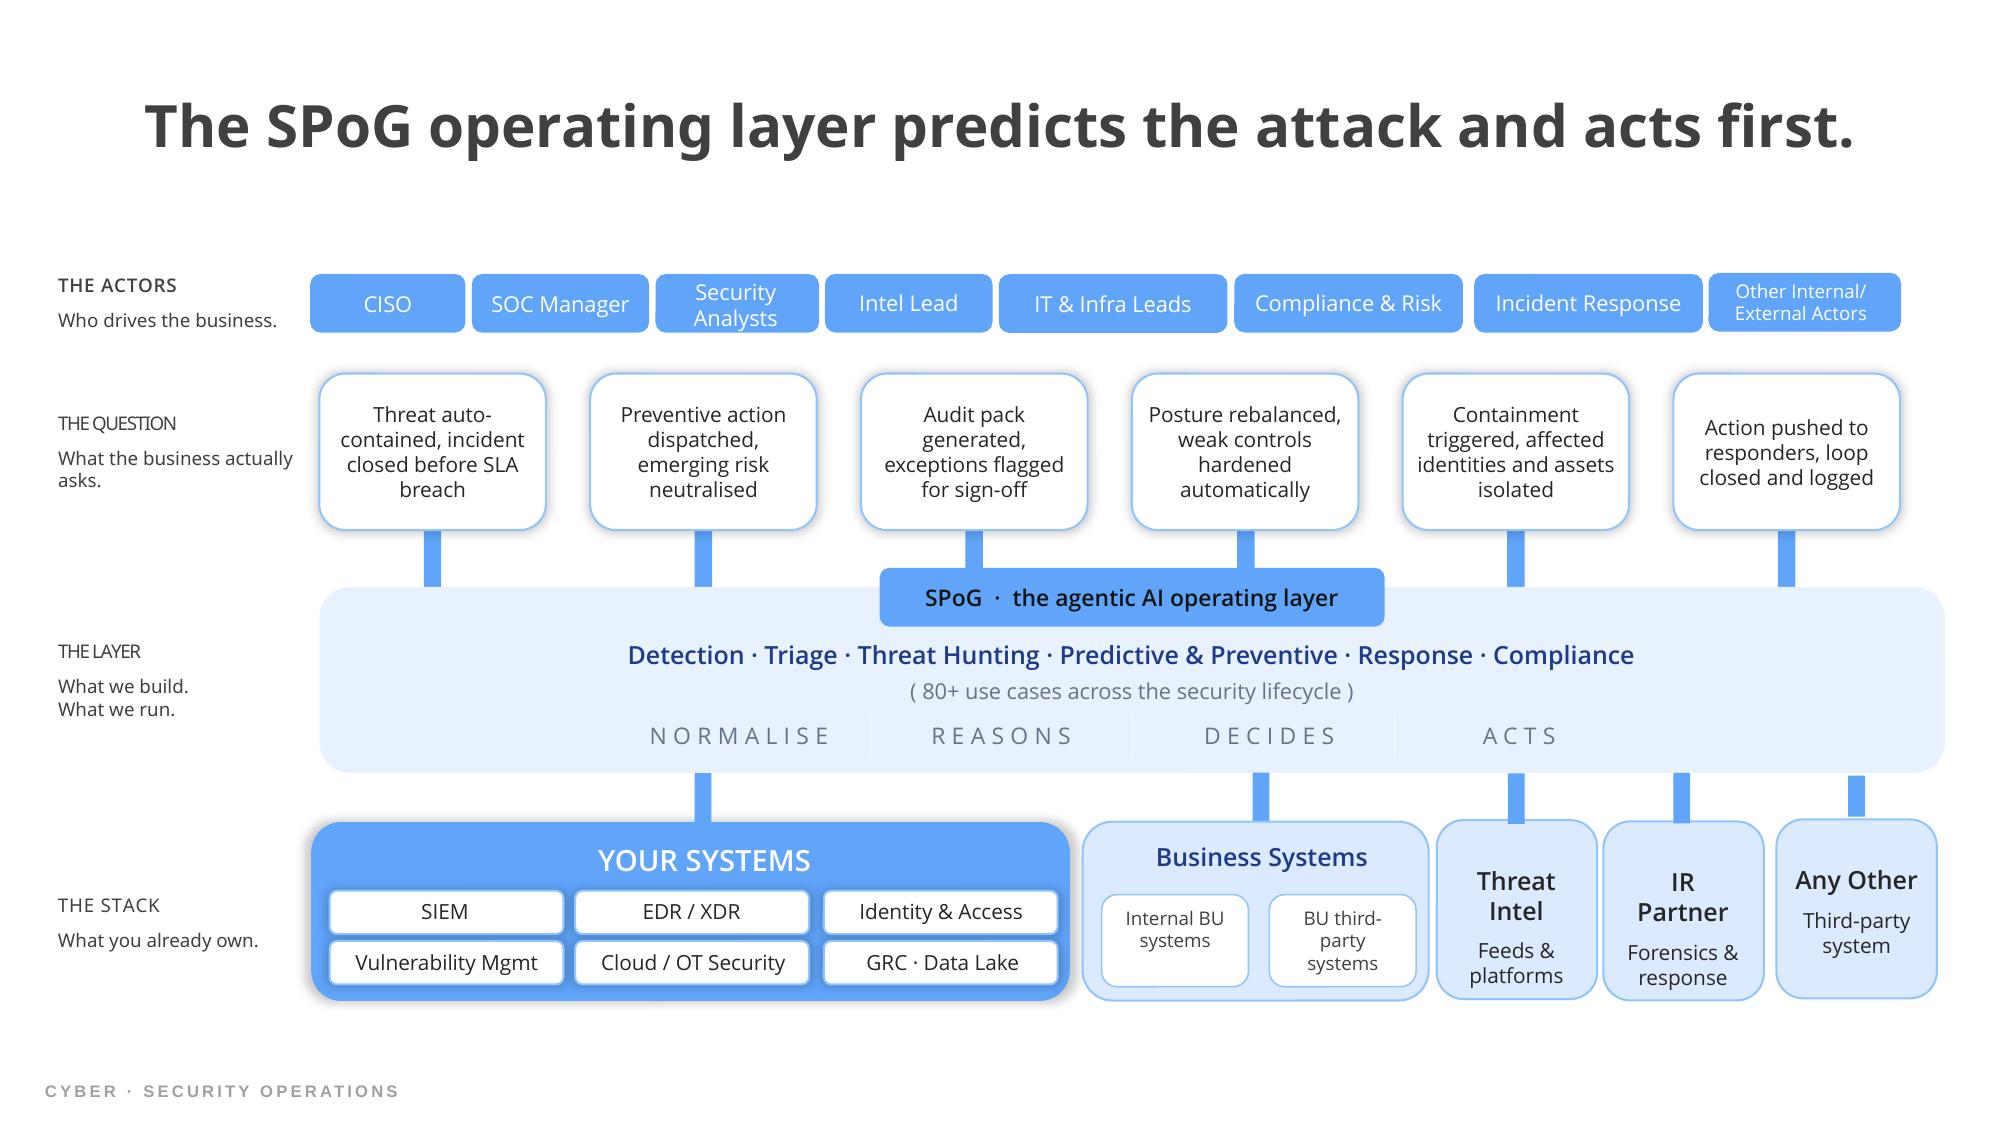
It is a horizontal intelligence layer that connects, correlates, reasons and acts across your complete cyber security ecosystem.
Federates Data
Endpoint, Network, Cloud, Identity and OT / IoT
Correlates Events
Transform isolated alerts into threat-level context.
AI Threat Reasoning
Intelligent prioritisation and recommendations.
Automated Response
Execute response playbooks automatically.
Business Risk
Translate technical signals into executive insights.
60%
Reduction in Mean Time to Detect
40-60%
Faster Incident Containment
24×7
Cross-Domain Threat Correlation
AI
Automated Response Playbooks
100%
Business Risk KPIs
Threat Detection & Response
Faster and more accurate detection using AI-driven correlation and automated containment.
Analyst Efficiency & Scale
Reduce alert fatigue, automate tier-1 response and increase analyst productivity.
Executive Confidence
One trusted, real-time risk picture for boards and CISOs.
Compliance & Audit Readiness
Support ISO 27001, NIST, SOC 2, GDPR and future frameworks.
Signals in. Threats out. The same engine, tuned for cyber.
Beneath every security decision sits one intelligent operating layer that connects, reasons and orchestrates every response.
Cyber Security
Fast. Seamless. High-Impact.
A proven delivery engine for security transformation.
Operating Model Design
Align people, tools and data into a future-ready security operating model that is unified, governed and strategic.
Single Pane Integration
Connect SIEM, EDR, Firewall, Cloud, Identity and Threat Intelligence feeds into one contextual operating layer.
AI-Led Automation
Deploy Agentic AI to automate alert triage, threat correlation, impact assessment and response playbooks.
Continuous Value
Continuously optimise your security posture through playbooks, advisory services and measurable operational outcomes.
Outcomes the board can measure.
Mean Time To Detect
Faster cross-domain threat identification within the first two quarters.
False Positives
AI correlation replaces manual triage, allowing analysts to focus on genuine threat response.
Audit-Ready Evidence
Every decision is traceable to the signals, policies and controls behind it.
A security operating model. Not another SIEM.
Cyber SPoG is a super-horizontal, AI-enabled operating model that optimises the whole security operation. Built on your stack. Evidence-first. Outcome-led.
Built On Your Existing Security Stack
Integrate SIEM, EDR, SOAR, Firewall, Cloud Security, Identity and Threat Intelligence into one operating layer. No rip-and-replace. One real-time security view.
Evidence-First Security
Every alert, compliance control and risk indicator is backed by live security data, ownership and repeatable workflows.
How to get started.
A structured, outcome-focused approach that identifies opportunities, validates impact and delivers measurable results within weeks.
- ✔ Schedule a discovery session with security and technology leadership
- ✔ Identify 3–5 high-impact use cases to prove the approach
- ✔ Define success metrics (MTTD reduction, false positive rate, compliance coverage)
- ✔ Launch a focused pilot to deliver measurable outcomes within weeks
Running today in regulated enterprises.
"SPoG transformed how our teams respond to incidents. Everything is visible in one place."
Head of Network Operations
"The reduction in operational noise has been significant. Our engineers focus on outcomes, not dashboards."